 Odoo 18 · 19
Access Audit & Explain
"Why can this user see it — or not?" Get the answer in seconds, with the exact group chain and record rule behind it, confirmed by Odoo itself.
Read-only — it never changes a group, an access right or a rule.
The problem
In Odoo, access is decided in four places at once: access rights, record rules, menu groups and field groups — and groups imply other groups. When someone cannot open an invoice, or can delete something they shouldn't, finding the reason means reading domains and group chains by hand.
The answer
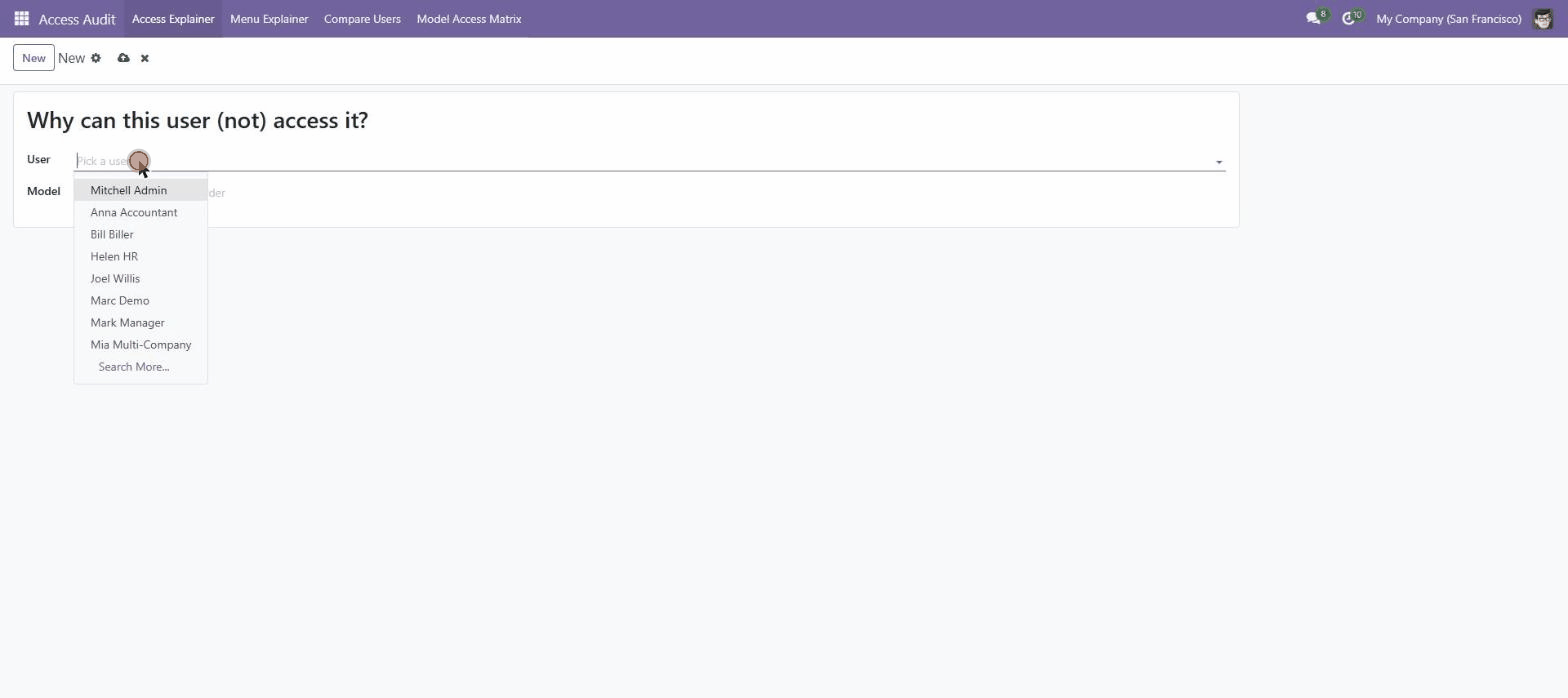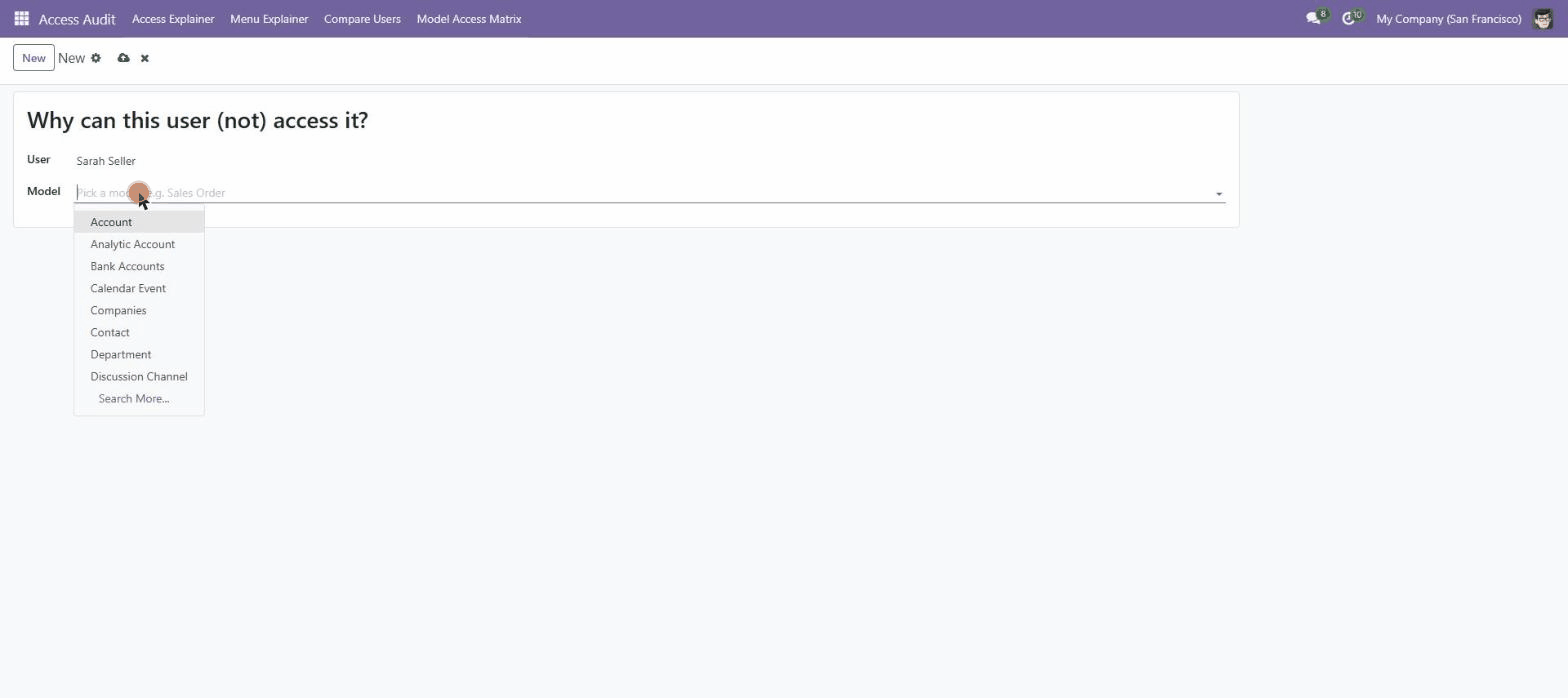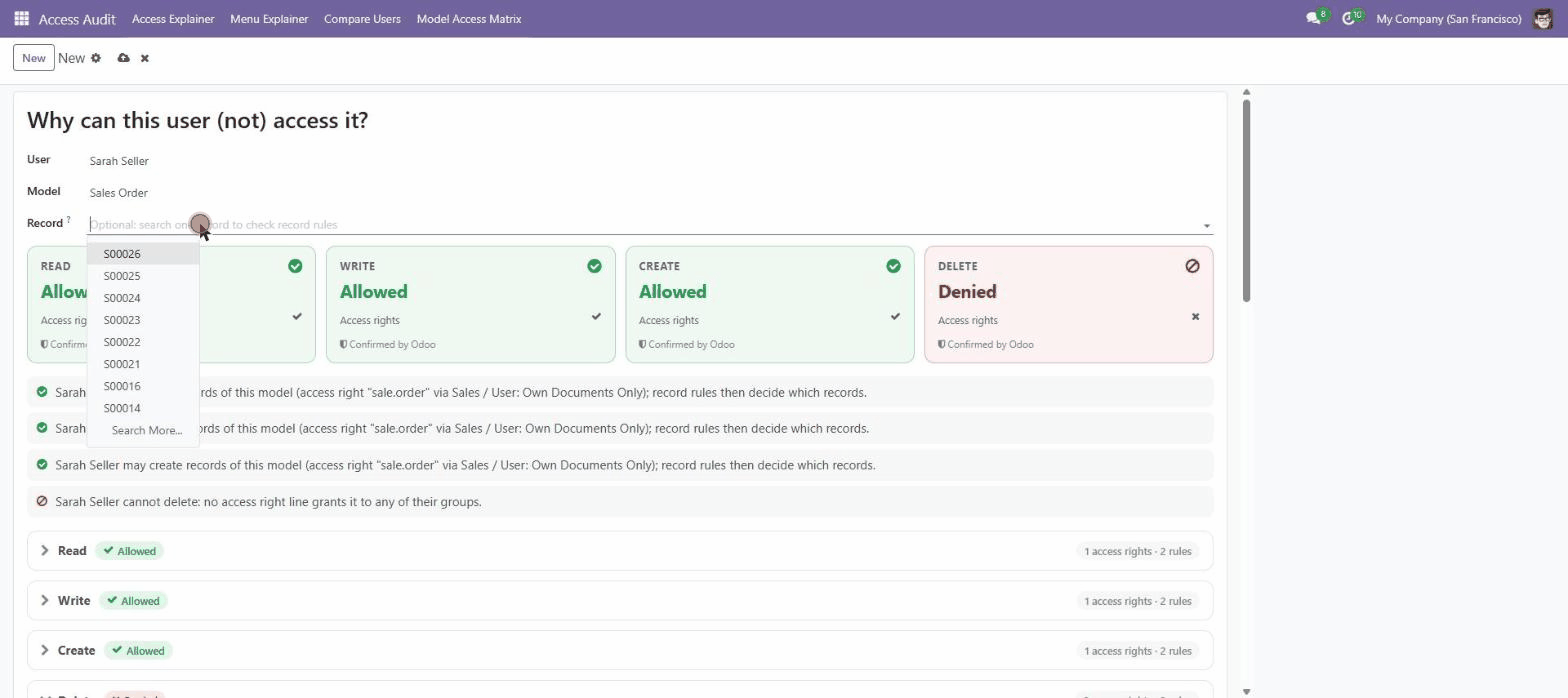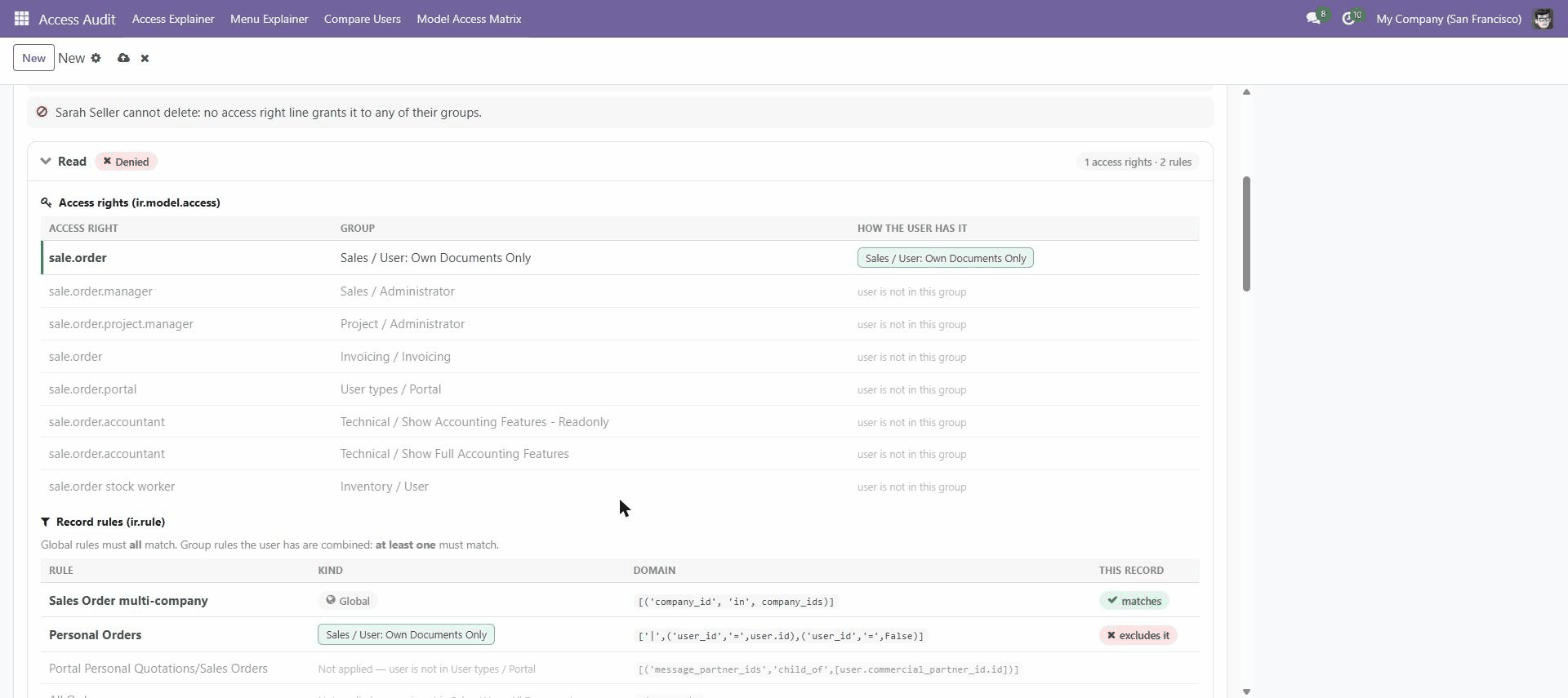
Pick a user and a model, and optionally a record. You get the verdict for read, write, create and delete, the access right that granted it, the chain of groups the user holds it through, and the record rule that let them in or kept them out — each verdict double-checked with Odoo's own access check.
Everything you need to debug access
1. Access Explainer
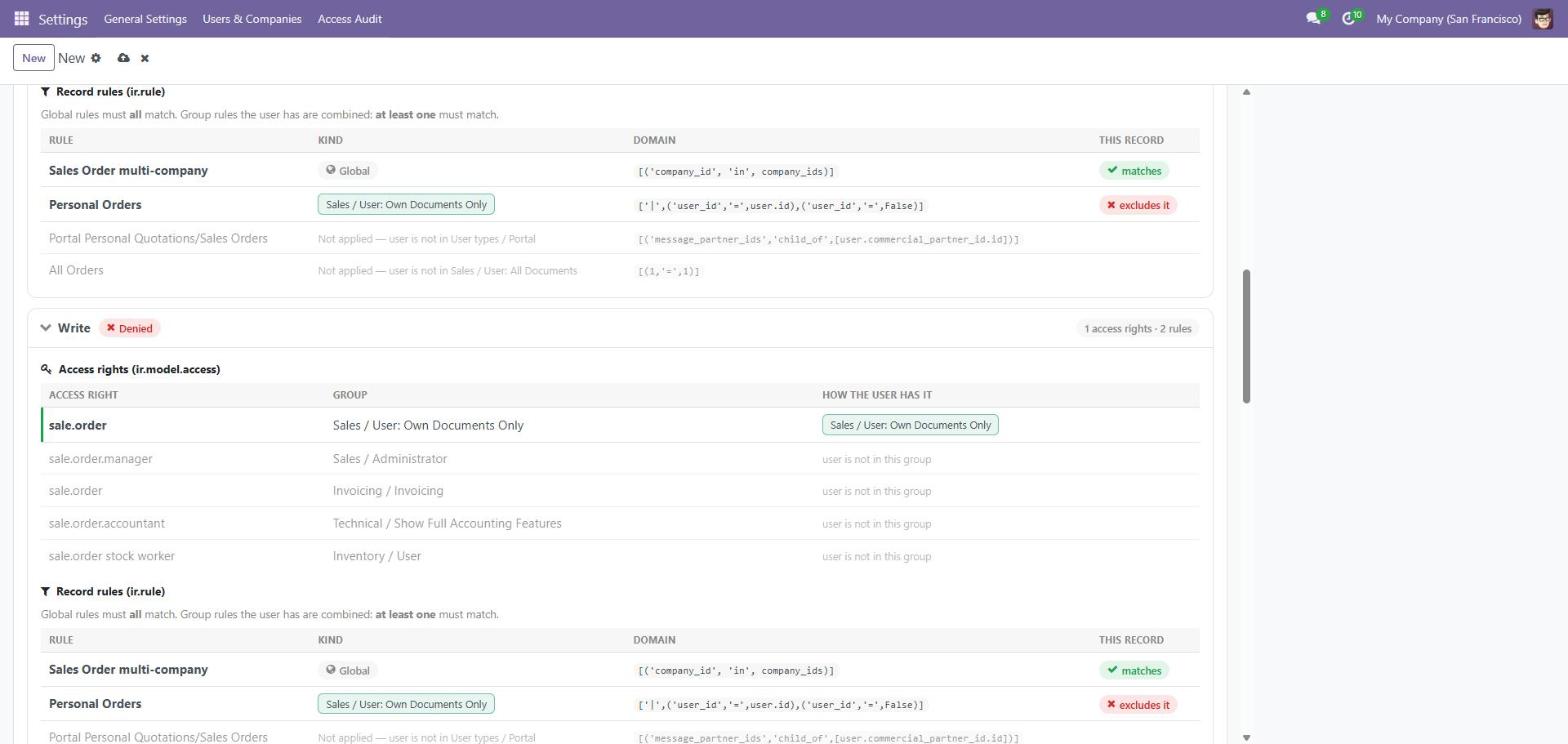
- Verdict for read / write / create / delete, with the reason
- Group chain, e.g. Sales Administrator → All Documents → Own Documents Only
- Record rules split into global (all must match) and group (one must match)
- Pick a record: see which rule matches or excludes it
- Restricted fields shown or hidden for the user
2. Menu Explainer
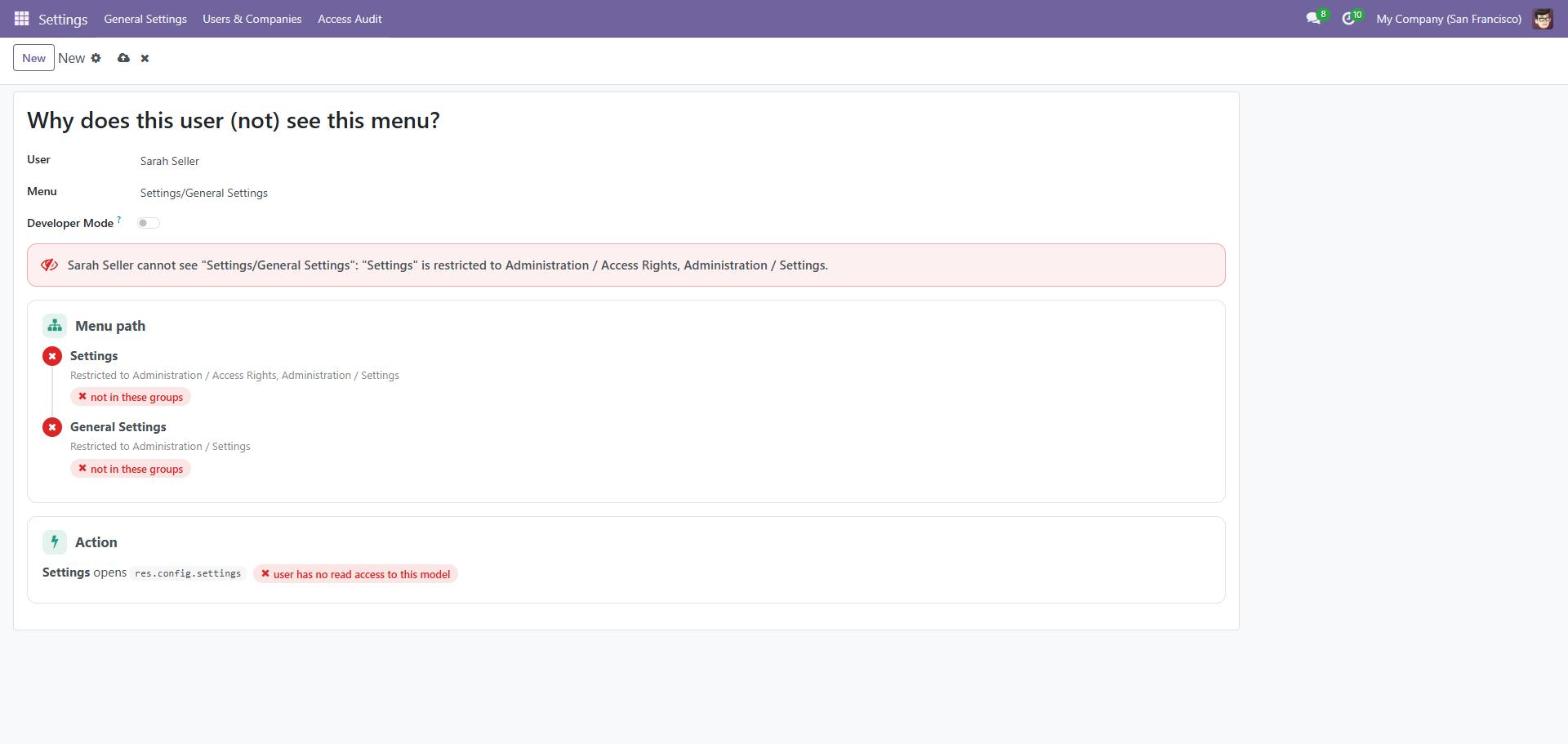
- Why a menu is shown or hidden for a user
- Group check on the menu and every parent
- Read access on the model the menu opens
- Folder menus: which sub-menus make them visible
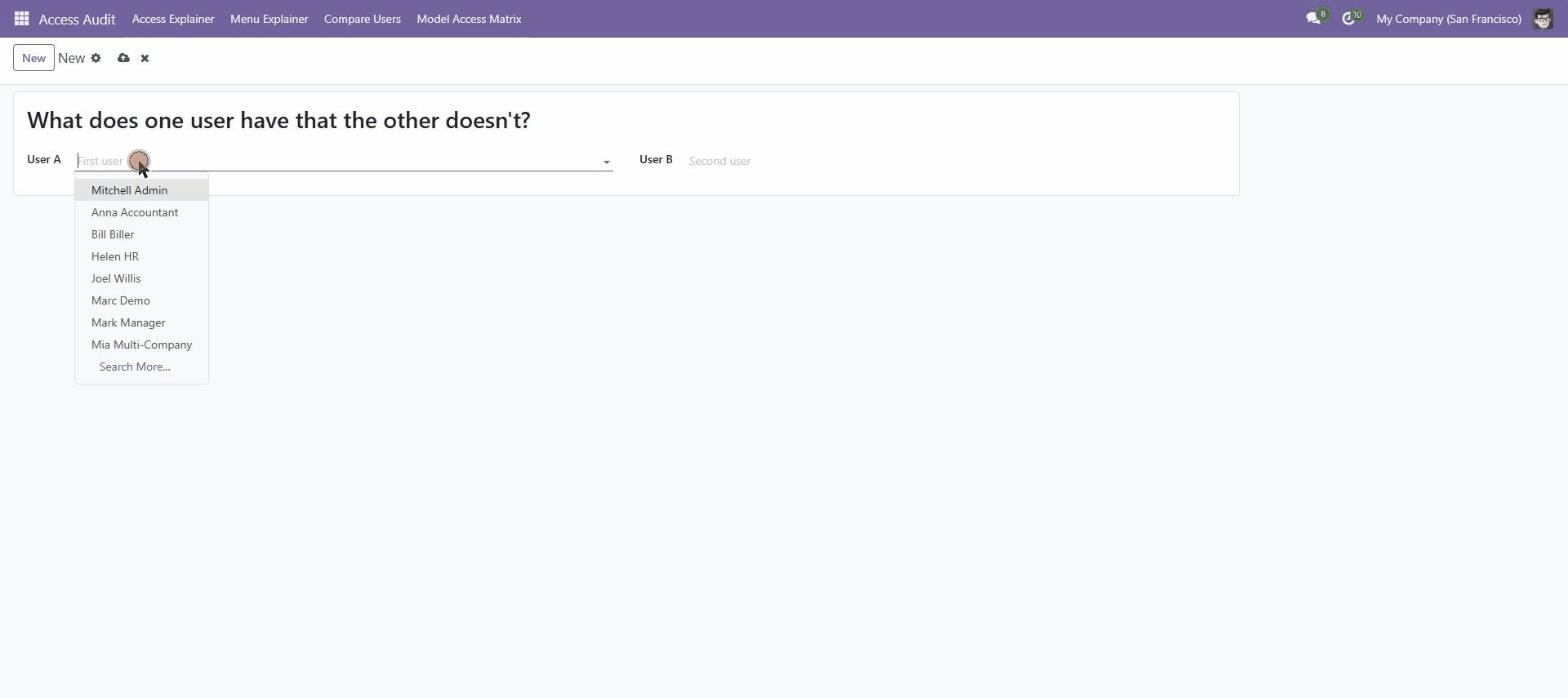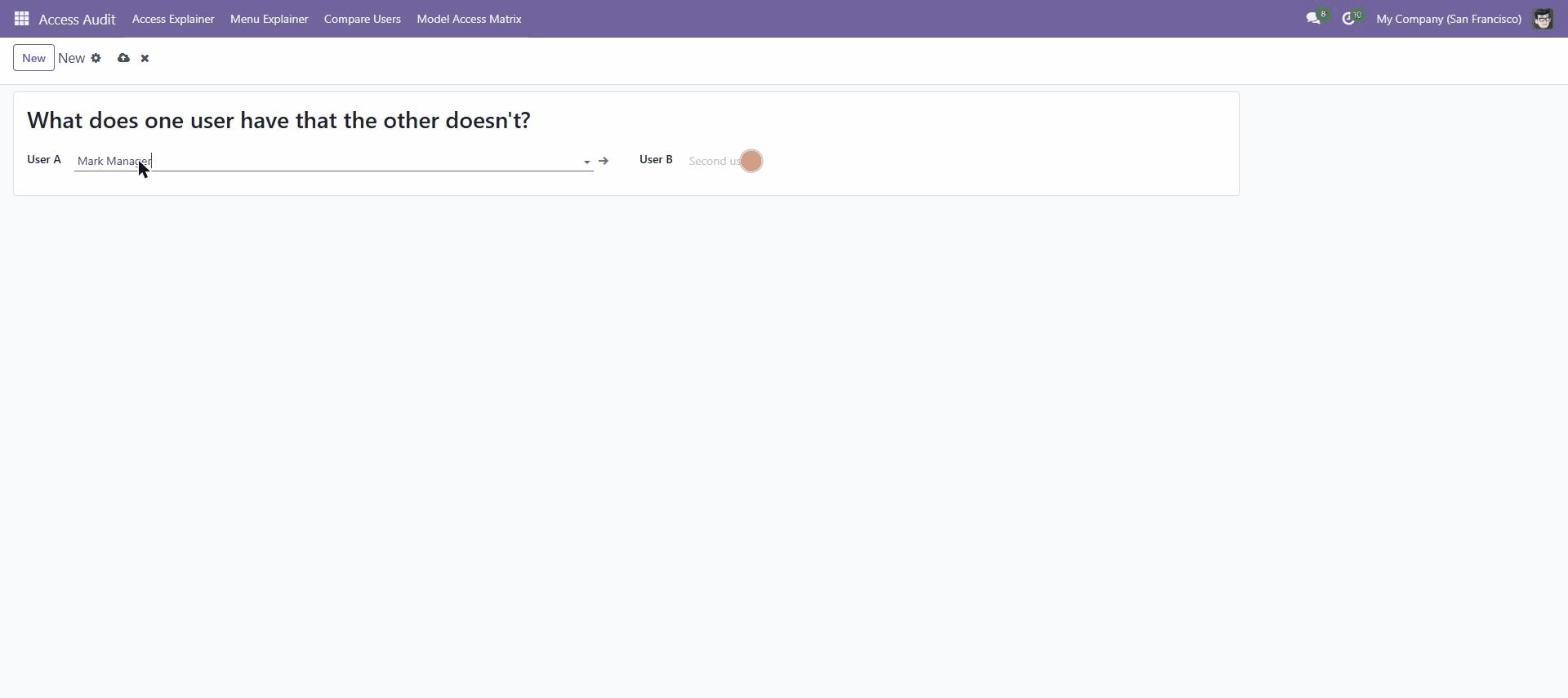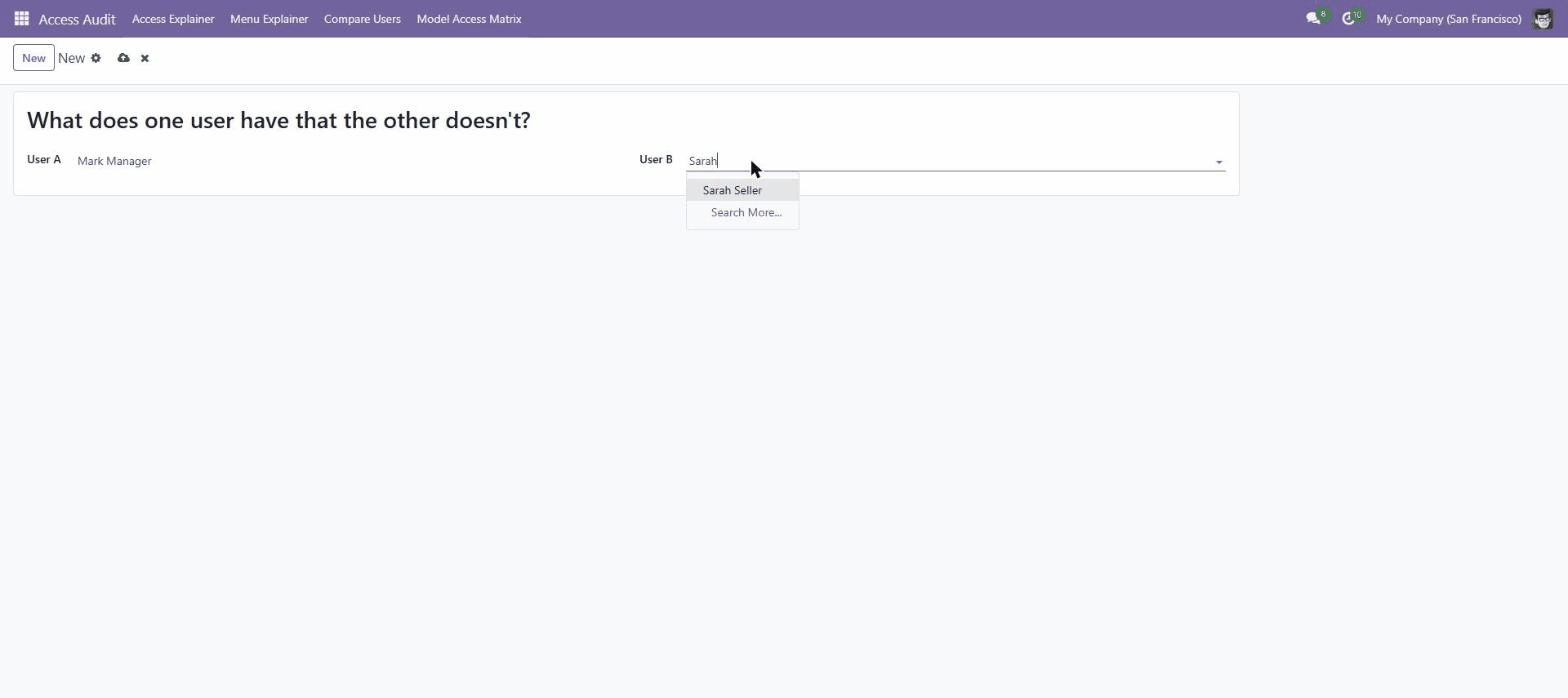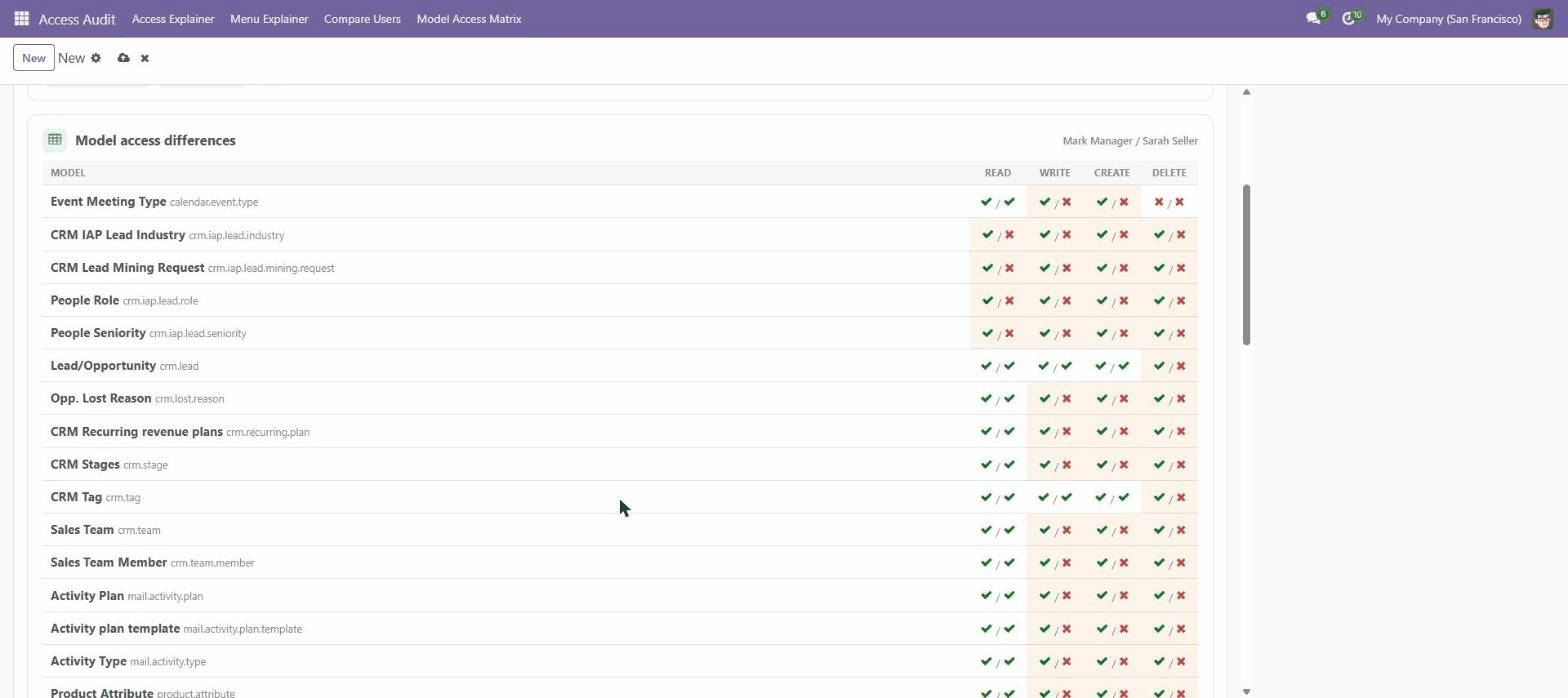
3. Compare Users
- "What does the manager have that the new hire doesn't?"
- Groups only one of them has
- Every model where their rights differ
- Rules and menus that apply to only one of them
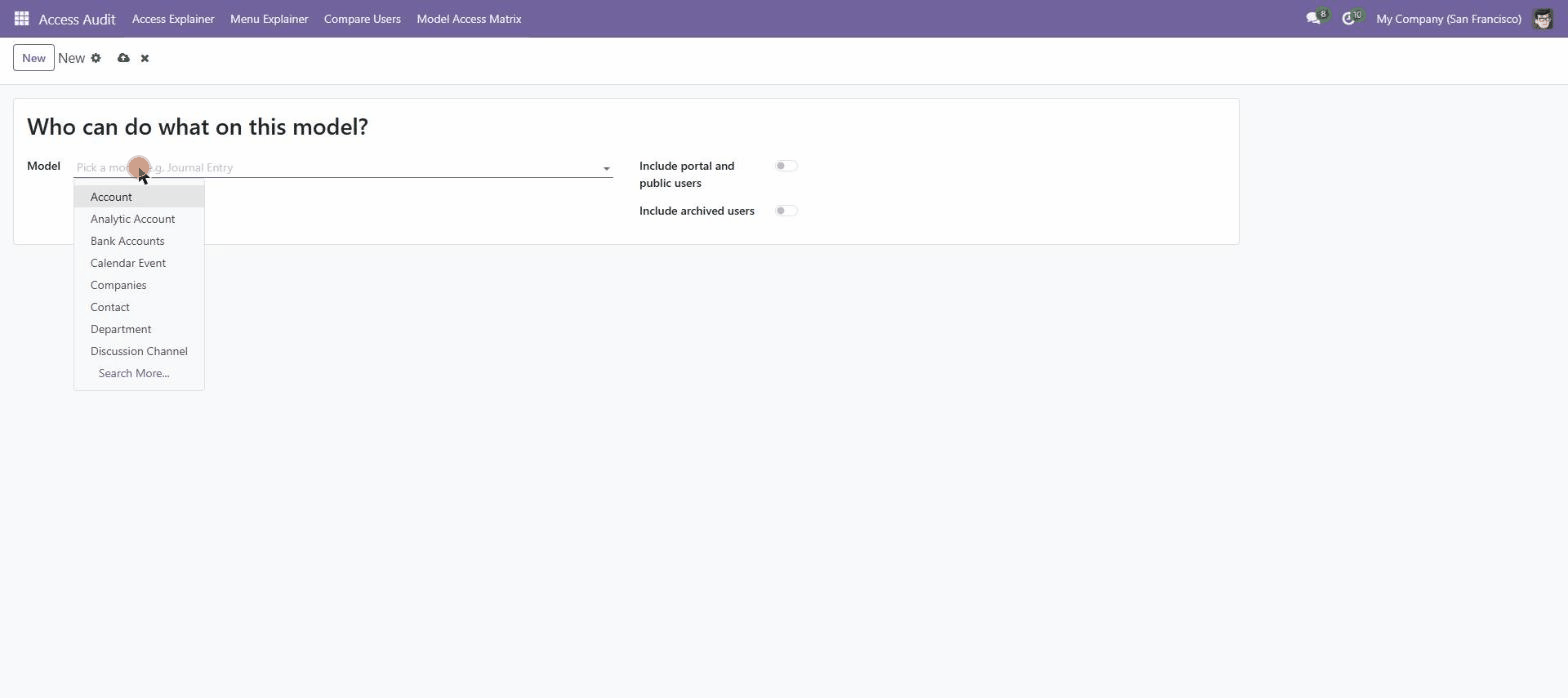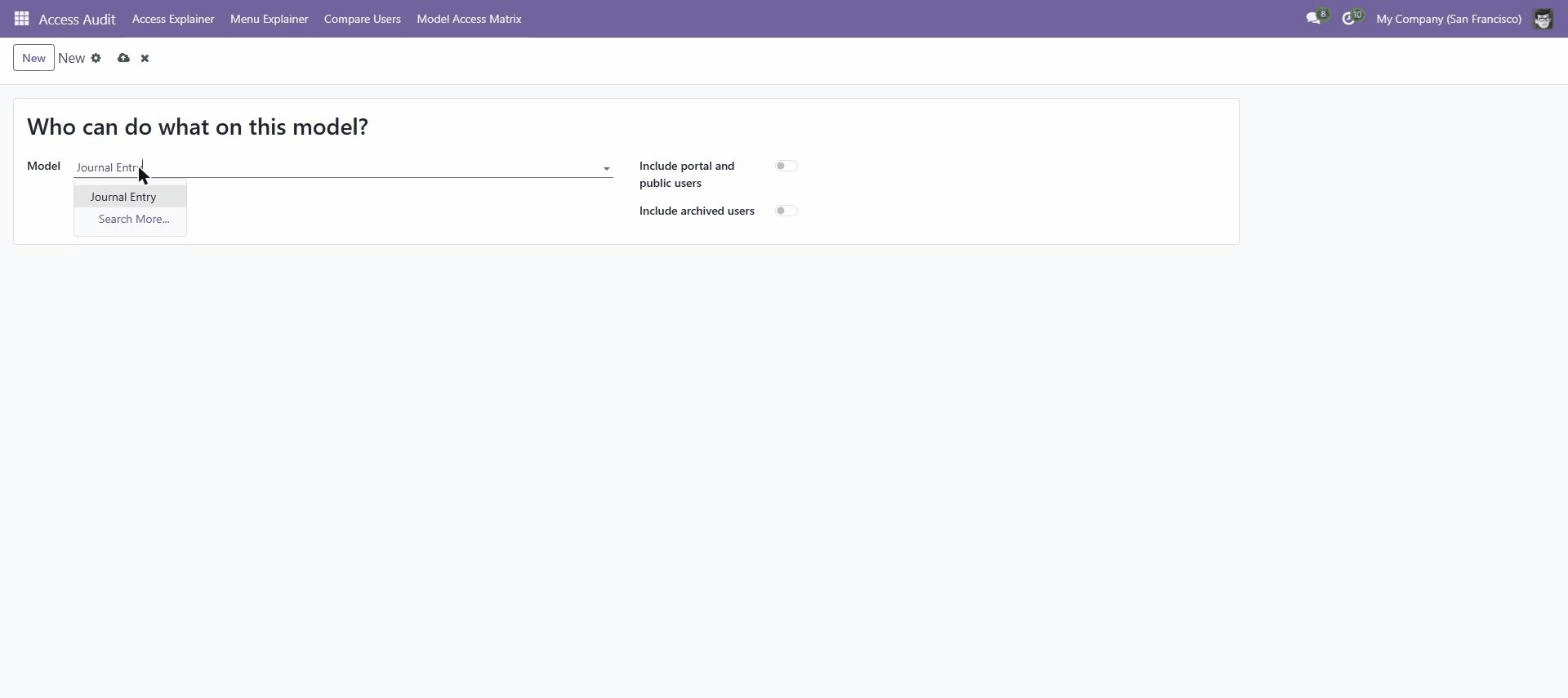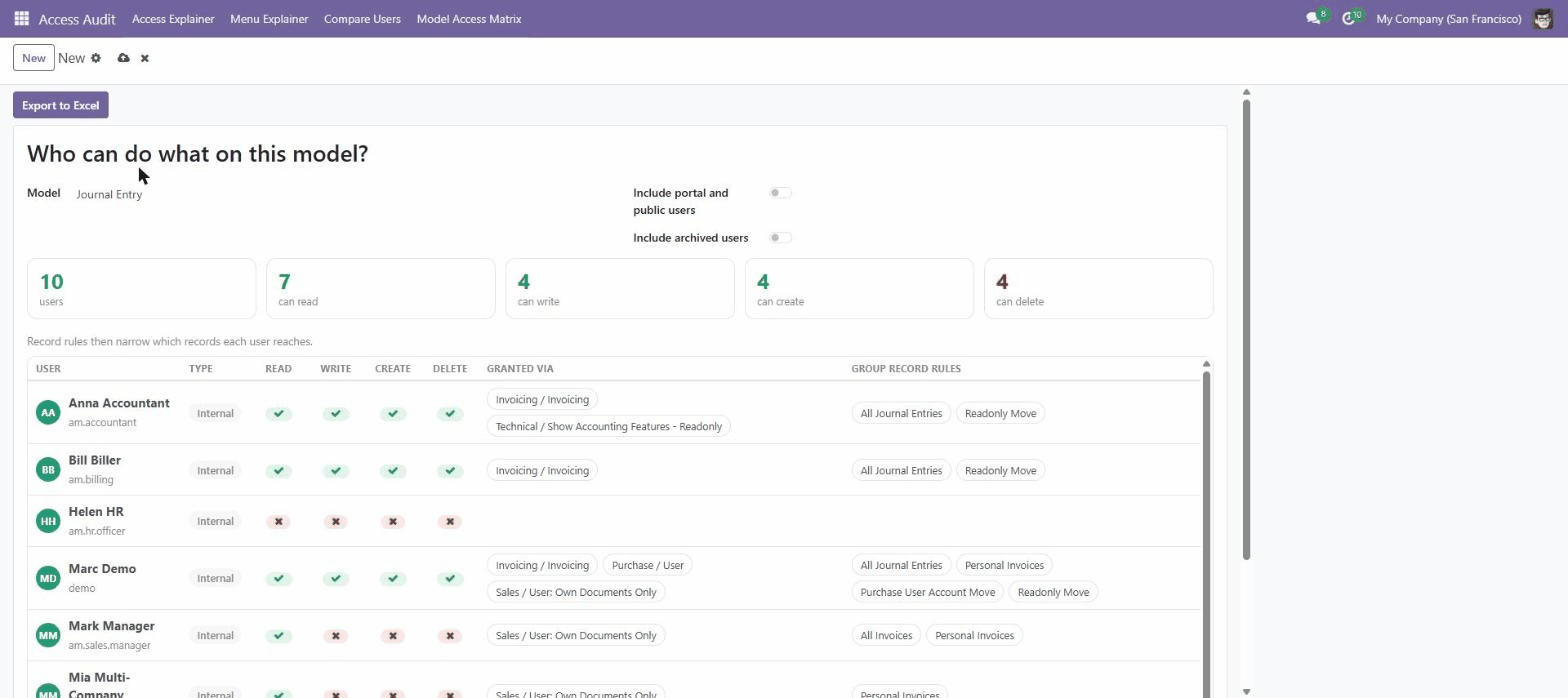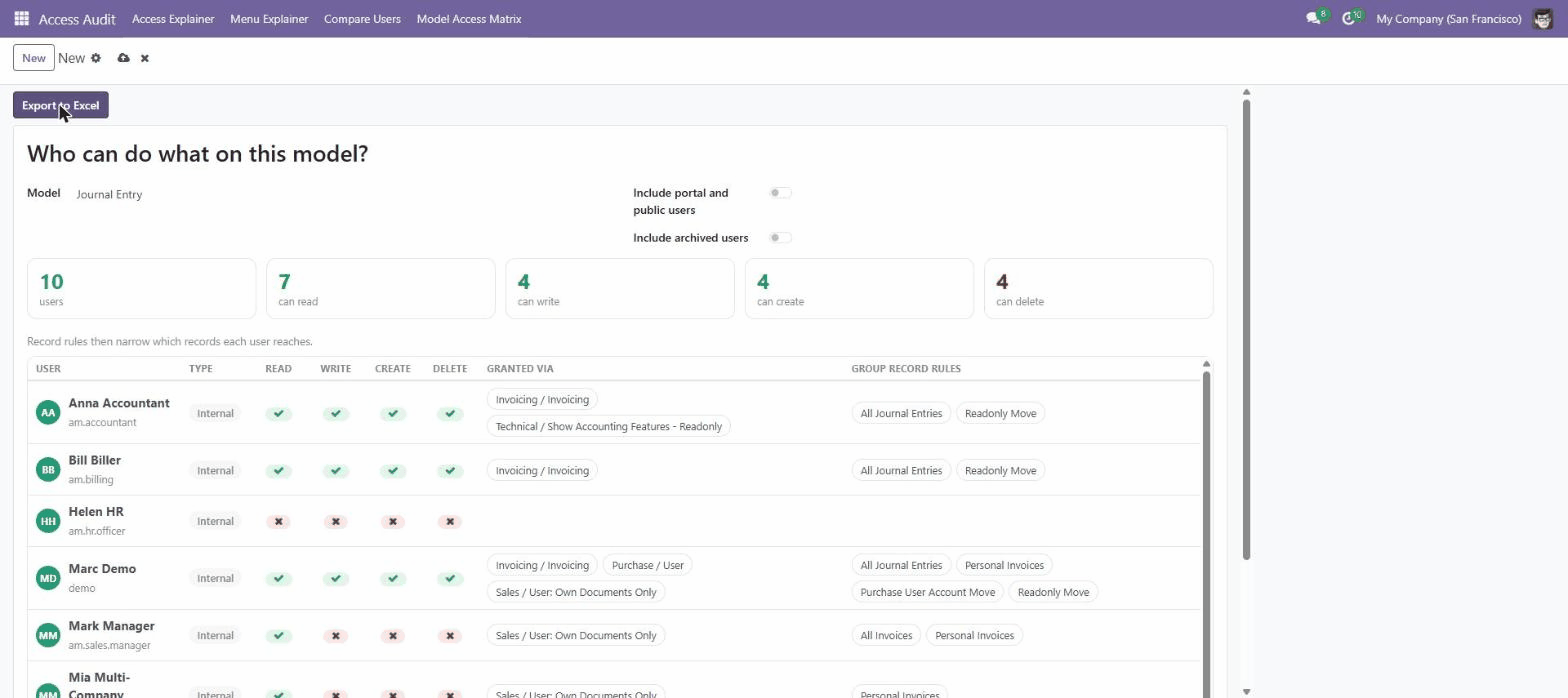
4. Model Access Matrix
- "Who can delete journal entries?" — one row per user
- Rights, granting groups and rules applied
- Optionally include portal, public and archived users
- Export to Excel for access reviews (ISO 27001, SOX, GDPR / KVKK)
Safe to install
Strictly read-only. Only Settings administrators and the new Access Auditor group can use it.
Answers you can trust
Every verdict is compared with Odoo's own check. Verified on 20,000+ user × model × operation combinations during development.
Built for
Administrators, implementation partners and consultants who debug access daily — and auditors who need a review they can file.
Technical details
| Odoo versions | 18.0 and 19.0 |
|---|---|
| Tested on | Community edition |
| Dependencies | base only |
| Hosting | Odoo.sh or on-premise |
| Languages | English, Türkçe |
| Multi-company | Supported |
| License | Odoo Proprietary License v1.0 |
| Price | €40, one-time |
Questions
Does it change any of my security settings?
No. It only reads groups, access rights, record rules and menus. Nothing is written except the temporary screens you open.
Can I use it on Odoo Online?
Standard Odoo Online does not allow third-party modules. Use Odoo.sh or your own server.
Does it work on Enterprise?
It depends only on the base module and we test it on Community. If you run into anything on Enterprise, write to us and we will look at it.
What if a model checks access in Python code?
Some models add their own checks on top of rights and rules. When Odoo's answer differs from the rights and rules, the screen says so instead of guessing.
Who can open it?
Settings administrators, plus anyone you add to the Access Auditor group — useful for an auditor who should not have full admin rights.
Stop guessing who can see what
€40 once. Questions before buying? We answer within one business day.